Home / TLS, SRTP, identity, and abuse / Hardening a SIP edge
Hardening a SIP edge
A defensive edge limits peers, requires digest and TLS, strips PAI, and does not share SRTP keying across legs.
Learn in 5 minutes
- Write an allow list of signaling peers
- Require digest on REGISTER and a domain certificate on TLS
- Keep identity and media keying rules explicit
Visual
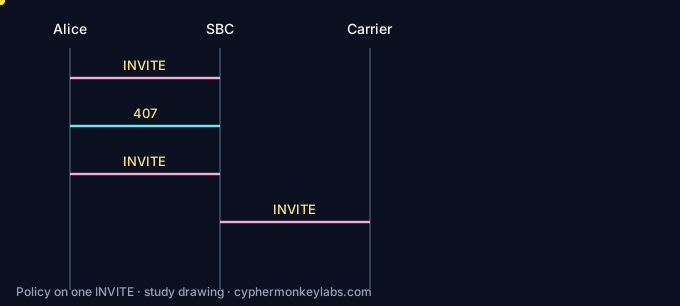
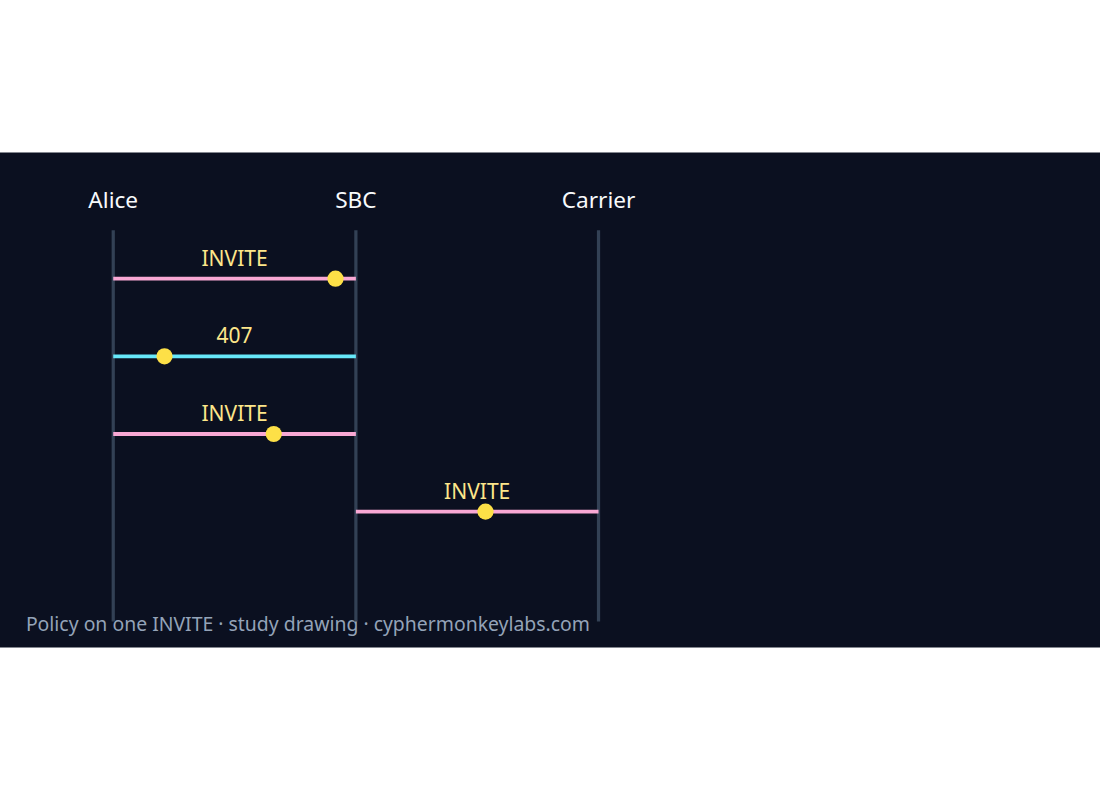
Each control answers a different failure. Removing one does not make the others optional.
Worked example
Checklist, not a device stanza Read the teaching checklist. It is not a vendor configuration and it is not a router QoS policy.
- Read each numbered line.
- Name the RFC for the certificate line.
- Name the header that answers a 407.
Fault
Operators cleared a scanning alarm by accepting every REGISTER. A new Contact appears for alice@example.com.
REGISTER without a challenge is how an unexpected Contact gets stored. That is the hijack class.
Quiz
Ecosystem
Glossary, sister systems, and the integration seam for this room.
Workforce management WFM forecasts volume and builds schedules. It consumes contact-center events. It does not parse Via headers. When a forecast is wrong, the SIP symptom is usually queue delay and 480 or carrier congestion, not a broken dialog ID.
Programmable communications APIs Twilio’s docs home is API reference, tutorials, and integration for Twilio products. Elastic SIP Trunking is the SIP-shaped product already cited in this lab. This page does not define the word CPaaS from an RFC. Read the vendor page before you copy a diagram that uses that word.
Sources and go deeper
- RFC 3261 §22 — last checked 2026-10
- RFC 7616 — last checked 2026-10
- Cisco CME toll-fraud prevention — last checked 2026-10
- RFC 5922 — last checked 2026-10
- RFC 3325 — last checked 2026-10
- RFC 8224 — last checked 2026-10
- RFC 3711 — last checked 2026-10
- FCC call authentication — confirm